Стандартна перевірка файлів пропустила небезпечну підміну, яка зараз використовується в реальних атаках.
У WordPress виявлено критичну вразливість, яку хакери вже використовують для завантаження виконуваних PHP-файлів без автентифікації. Вразливість криється в плагіні Bricksforge, і Patchstack присвоїв їй максимальний бал серйозності 10.
Вразливість CVE-2026-85097 впливає на Bricksforge версії 3.1.8.9 та раніші; розробники виправили проблему у версії 3.1.8.10. Bricksforge розширює функціональність візуального редактора Bricks Builder, додаючи форми, анімацію та інтерактивні елементи.
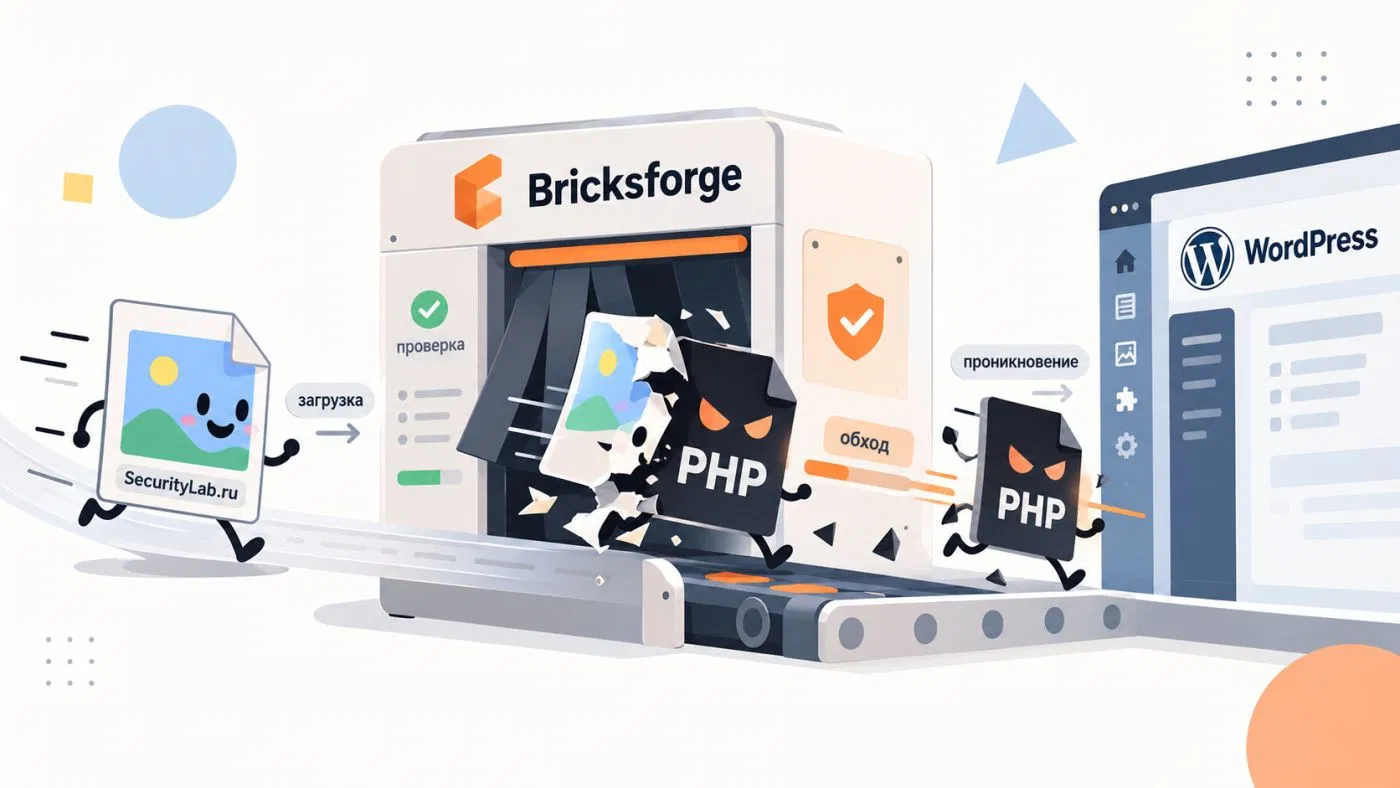
Проблема виникає через параметр `temporaryFileUploads`. Під час початкового завантаження Bricksforge перевіряє MIME-тип, але згодом довіряє шляху до файлу, наданому браузером. Зловмисник може використати це, щоб створити невідповідність між перевіреним вмістом та кінцевим ім'ям файлу.
Щоб виконати атаку, зловмисник спочатку отримує одноразовий номер через неавтентифікований обробник AJAX, а потім завантажує гібридний GIF-файл, що містить вбудований PHP-код. Перевірка системи ідентифікує файл як дійсне зображення. Потім зловмисник замінює URL-адресу в метаданих на шлях, що закінчується розширенням `.php`. Як наслідок, сервер може зберегти вміст зображення як виконуваний скрипт.
For the final stage, it is most common to use the REST API at the address /wp-json/bricksforge/v1/form_submit. Running an encoded PHP file allows you to export commands to the server, place web shells, and modify the site. A WordPress account is not required for operation.
Patchstack first flagged the service failure on June 7, 2026 at 21:47 UTC. The fakers registered requests from 63 unique IP addresses. One group with 44 addresses sent 56 new requests in a matter of seconds, and three other addresses verified 25 variants of PHP extensions and their encoding.
In 95% of requests, the path to the output file ended in .gif or .png, which is why the end addresses often pointed to a PHP script. The extensions .php5, .phtml, different case options and encoded characters have been expanded. In addition, the tests were directed directly to the creation of the login_admin_*.php files in the standard WordPress folder.
Patchstack described the mechanics of the attack and talked about the RapidMitigate rule. However, the number of files and IP addresses is not comparable to the number of malicious sites. The CVE registry scored 9.8 for exposure, while Patchstack rated it at 10.
Administrators are recommended to install Bricksforge 3.1.8.10 or the latest version. If the site is working on a new collection, you should check the request logs to see the form submission form, folders and PHP files that have recently appeared. Similar attacks have previously occurred in the Elementor Pro and Super Forms plugins, where unsafe attacks also led to the destruction of the code.
 Freelance
 Graphic & Design
 Product People and Teams
 Програмування та техн